Category: Uncategorized

  • How to Create Email Templates Securely and Effectively

    How to Create Email Templates Securely and Effectively

    When you’re creating an email template, it’s easy to jump straight to the design and copy. But before you even think about colors or calls-to-action, there's a more critical first step: building a solid foundation of email privacy and security.

    A great template isn't just about looking good—it's about earning trust. Every link, every image, and every piece of data has to be handled in a way that protects your recipient and builds their confidence in your brand. A secure template is essential for protecting your audience from phishing, data leaks, and other cyber threats.

    Building a Foundation for Secure Email Templates
    A laptop open on a wooden desk with a green security key, documents, and "Secure Foundation" logo.

    Learning how to create an effective email template starts with a security-first mindset. Think of it this way: the most beautiful email in the world is useless if it lands in the spam folder, leaks private data, or makes your recipients feel unsafe.

    This means making conscious decisions from the very beginning to protect both your audience and your reputation. One of the most important of these foundational choices is whether to send emails yourself or use a dedicated, hosted email platform built for security.

    The Role of Hosted Platforms in Security

    Sending emails directly from your own server might seem like the simplest route, but it's a minefield of potential security and deliverability problems. This is where hosted email platforms like Typewire come in. They are purpose-built to handle these complexities, giving your communications a secure and reliable home.

    These services do the technical heavy lifting for you, ensuring everything you send meets strict industry standards for both privacy and security. That professional handling is what separates a legitimate, secure email from one that gets flagged as spam or poses a risk to recipients.

    Here’s what you get by using a security-focused hosted platform:

    • Managed Infrastructure: They handle the servers, IP reputation management, and authentication protocols (like SPF, DKIM, and DMARC) that are absolutely essential for good deliverability and preventing email spoofing.
    • Built-in Security: You'll often find features like automatic HTTPS on all tracking links, secure hosting for your images, and dynamic content sanitation to block common vulnerabilities like cross-site scripting (XSS).
    • Compliance and Best Practices: A reputable platform keeps up with ever-changing email standards and privacy laws (like GDPR and CCPA), which takes a huge compliance weight off your shoulders.

    A hosted email platform is essentially a secure intermediary. It’s like having an expert security team dedicated to your email delivery, making sure every message is authenticated, compliant, and trustworthy before it ever hits a single inbox.

    Adopting a Privacy-First Mindset

    "Privacy-first" isn't just a trendy phrase; it’s a practical strategy for building a communication channel people can rely on. When you put user privacy at the forefront of your template creation process, you naturally create a better, more secure experience that encourages genuine, long-term engagement.

    For example, consider how images are loaded in an email. When a recipient opens your message, the image download can reveal their IP address, location, and device details to the server hosting the image. A secure platform can serve as a proxy for these images, effectively shielding that user data from third-party servers. It’s a small detail that makes a big difference in protecting user privacy.

    This mindset should influence your content, too. Every link must point to a trustworthy, HTTPS-secured destination. Any personalized data you use has to be handled with extreme care to prevent leaks. And your unsubscribe process needs to be dead simple and honor user requests immediately.

    By building your templates on a foundation of respect for user privacy and robust security, you're doing more than just improving deliverability—you're cultivating a loyal audience that trusts you. This is the real first step to creating email templates that actually work.

    Designing for User Trust and Engagement
    A person's hand writes on a document with diagrams and text on a wooden table, next to a laptop displaying charts.

    Once you’ve got your security strategy sorted, it’s time to bring it to life visually. Great email design is so much more than pretty colors and fonts; it's about creating a predictable, trustworthy experience that shows you respect your users' privacy and security. Every single element, from your layout to your typography, plays a role in how someone perceives your brand’s credibility.

    The key is to design with clear intention. You want to guide the reader’s eye, make the information easy to scan, and subtly communicate that their security is a top priority. Steer clear of cluttered layouts or confusing navigation—these can instantly create a sense of unease and make your email feel unprofessional or, worse, like a phishing attempt.

    Building Trust Through Predictable Layouts

    A consistent, intuitive structure is the bedrock of user trust. When someone opens your email, they should feel a sense of familiarity, especially if they’ve heard from you before. This predictability makes your message feel safer and more legitimate because it doesn’t require them to overthink its authenticity.

    The best way to achieve this is with a strong visual hierarchy. Use clear headings, generous white space, and logical content blocks to walk the reader through your message. When you create email templates with a consistent header, footer, and branding, you establish a recognizable pattern that users subconsciously learn to trust, helping them distinguish your legitimate emails from phishing scams.

    This is non-negotiable for transactional emails like password resets or purchase confirmations. People have a very specific expectation for what these should look like, and any weird deviation is an immediate red flag for a security threat.

    Avoiding Deceptive Design Patterns

    In the race for clicks and opens, it’s tempting to use "dark patterns"—design tricks that mislead users into doing things they didn't mean to. Let me be clear: these tactics are the fastest way to obliterate trust, violate user privacy, and will wreak havoc on your deliverability.

    Here are a few common deceptive patterns you absolutely must avoid:

    • Hidden Unsubscribe Links: Burying the unsubscribe link in tiny, light-gray text at the very bottom is a classic. Always make it obvious and easy to find to respect user choice and comply with anti-spam laws.
    • Misleading Subject Lines: Clickbait that has nothing to do with the email's content will only annoy people and earn you a one-way ticket to the spam folder.
    • Confusing Button Text: Using vague language on your calls-to-action ("Continue") can trick people into clicking something they wouldn't have otherwise. Be specific ("Complete Your Secure Purchase").

    A trustworthy design is an honest one. Your layout should empower users by making their choices clear, not manipulate them into engagement. Real engagement comes from providing genuine value, not from trickery that erodes privacy and trust.

    Email Client Design Considerations

    Every email client renders HTML and handles security a little differently. What looks perfect in Apple Mail might break in Outlook. This table gives you a quick rundown of what to watch out for across the big three, especially concerning privacy features that can impact your design.

    Feature Apple Mail Gmail Outlook Security/Privacy Implication
    Image Rendering Generally good; Mail Privacy Protection (MPP) pre-loads images via proxy. Excellent support; caches images through its own proxy server. Notoriously tricky; often blocks images by default and uses a different rendering engine. MPP and Gmail's proxy hide the user's real IP address and prevent accurate open tracking based on image pixels, enhancing user privacy.
    Responsive Media Queries Full support. Full support. Limited support, especially on Windows desktop versions. Can break mobile-first layouts. Inconsistent rendering can make an email look broken or unprofessional, eroding trust and potentially hiding important security information.
    Dark Mode Offers its own color inversion, which can alter your design's colors. Supports @media (prefers-color-scheme: dark) for custom dark mode styles. Varies by version; some auto-invert colors, others do not. If not properly tested, your text or images could become unreadable, creating a poor and untrustworthy user experience.

    Ultimately, you have to design defensively. Assume images might be blocked and that colors could be inverted. A robust, secure template is one that remains clear and functional no matter how the client decides to display it.

    Transparency in Tracking and Performance

    Email tracking, like monitoring opens and clicks, is standard practice, but how you do it matters more than ever from a privacy perspective. With privacy features like Apple's Mail Privacy Protection blocking tracking pixels, your design must function perfectly whether those pixels load or not.

    Using a secure hosted email platform to manage your templates often helps by handling tracking in a privacy-first way, such as routing images through a proxy to shield user IP addresses. It’s also just good practice to be transparent in your privacy policy about what you track and why. This honesty builds confidence and shows you respect your users' control over their data.

    Remember, your design choices have a massive impact on performance. With over 51% of emails being opened on Apple Mail and another 27% on Gmail, your templates have to render flawlessly on these platforms. Responsive design isn’t just a nice-to-have; it’s critical for reaching the nearly 4.6 billion email users worldwide. To see how this applies in practice, checking out a guide on building B2B lead nurture campaigns that convert can provide some fantastic, real-world strategies.

    Writing Secure and Compatible HTML

    Alright, let's get down to the code. This is where your design comes to life, but writing HTML for email is a whole different beast than building a webpage. Forget the latest CSS frameworks and modern tricks. Email development is all about building robust, secure, and universally compatible code that won't fall apart in the wild world of different email clients.

    The reality is, you're building for a fragmented ecosystem. From Gmail and Apple Mail to the notoriously picky Outlook, each client has its own quirky way of rendering HTML. Your mission is to write code that looks great everywhere, and that starts with a security-first mindset. It's not just about aesthetics; it's about building trust and protecting your recipients with every line of code.

    The Foundation of Compatibility: Tables for Layouts

    I know what you're thinking. Tables for layout? Didn't we leave that behind in the early 2000s? For web design, yes. For email design, tables are still king. They are the single most reliable tool in your arsenal for ensuring your layout holds together across every major email client.

    Think of tables as the scaffolding for your email. They create a rigid, predictable structure that prevents your carefully crafted design from collapsing into a jumbled mess in less capable clients like older versions of Outlook.

    • The Main Container: Kick things off with a single master table that wraps all your content. This is what sets the overall width and centers your email in the user's inbox.
    • Rows and Columns: Inside that main table, you'll nest other tables to create your content rows—header, body, footer, you name it.
    • Content Cells: Your actual text and images live inside table cells (<td>). This is how you guarantee alignment and proper spacing.

    It feels a bit old-school, I get it. But this method's universal support is precisely why it remains the industry standard. To build emails that work for everyone, you have to code for the lowest common denominator first. You can dive deeper into the nuances of various platforms by exploring our guide on what is an email client and why its rendering engine matters so much.

    Embedding Security Directly into Your Code

    A secure template doesn't happen by accident. You have to build it with intention from the ground up, actively looking for and closing potential security gaps as you write your HTML. This is especially true if you’re pulling in dynamic content or linking to external assets.

    The most important habit you can develop is enforcing HTTPS on every single link. No exceptions. Whether it's an image source (src) or a hyperlink (href), it absolutely must start with https://. This simple step encrypts the connection, protecting your users from man-in-the-middle attacks where a malicious actor could intercept or change the content in transit.

    Security isn't an add-on; it's a core component of the coding process. Sanitizing every piece of dynamic data and forcing secure connections on all assets are non-negotiable steps for building a template that protects both your brand and your audience.

    On that note, stay far away from scripts. Never, ever embed JavaScript or any other scripting language in your email. Nearly every email client blocks them on sight for security reasons, and their presence is a huge red flag for spam filters. Stick to clean HTML and inline CSS, and you'll be fine.

    Creating an Essential Plain-Text Version

    For every beautiful HTML email you build, you need a plain-text counterpart. This isn't just an afterthought—it's a critical part of a professional email strategy that enhances both security and privacy. Many people, particularly in corporate or high-security settings, set their email clients to block HTML by default. Without a plain-text version, your message is dead on arrival.

    A plain-text version is also essential for:

    1. Accessibility: Screen readers used by subscribers with visual impairments can parse clean, simple text far more reliably than they can navigate complex, table-based layouts.
    2. Deliverability: Spam filters get suspicious when an HTML email arrives without a plain-text alternative. Including one is a strong signal that you're a legitimate sender who follows best practices.
    3. User Choice & Privacy: Some people just prefer reading text-only emails to avoid tracking pixels and other potential privacy concerns. Giving them that option is a small but meaningful way to respect their preferences.

    While crafting your HTML, don't forget about making your images accessible, too. Learning about properly adding captions or alternative text to images is a key skill. This, combined with a solid plain-text version, ensures your email is inclusive and robust. Just make sure your plain-text version includes all the same crucial information and links as the HTML, formatted with simple line breaks to keep it readable.

    Testing and Deploying Through a Hosted Platform

    So, you’ve coded your template. It looks great on your screen, but it’s not really done until it survives in the wild. This last leg of the journey—testing and deployment—is where the rubber meets the road. It’s how you make sure your template is not just well-designed, but also secure, reliable, and ready for every inbox imaginable.

    This is exactly why a dedicated hosted email platform is a non-negotiable part of the process. Trying to send mass emails from your own server is a recipe for disaster, throwing you into a world of deliverability nightmares and security headaches. Hosted platforms are built specifically to handle this chaos, giving your emails a secure, optimized path to your audience.

    The Security Edge of a Hosted Platform

    When you use a professional service like Typewire, you’re not just getting a "send" button. You’re tapping into a level of security that’s practically impossible to build yourself. These platforms are engineered from the ground up to tackle the immense technical challenges of modern email, making sure your messages are both protected and delivered.

    Instead of getting bogged down in server configurations, you get a fully managed environment that handles all the critical security work behind the scenes. This means they’re constantly maintaining IP reputation, managing complex authentication protocols, and staying ahead of the latest anti-spam tactics.

    The security benefits are very real:

    • Managed Deliverability: Top platforms work tirelessly to maintain high deliverability rates. This isn’t just about getting into the inbox; it’s a security signal that proves you’re a legitimate, trusted sender.
    • Centralized Template Management: Your templates live in one secure, controlled spot. This simple feature prevents team members from accidentally using old, vulnerable versions or making unauthorized changes.
    • Automatic Link Security: Good platforms automatically enforce HTTPS on all tracking links. Many also proxy image requests to help protect user privacy by masking IP addresses.

    Your Pre-Deployment Checklist

    Before you even think about hitting send, you need to run your template through a rigorous testing gauntlet. This is more than just a quick spell-check; it’s a full-blown security audit to ensure every piece of your email works exactly as intended without creating any risks.

    I like to split my checklist into two key areas: rendering and security. Both are absolutely critical for building trust with your subscribers.

    Rendering and Functional Tests

    This is all about making sure your email looks and works perfectly for everyone, no matter what device or email client they’re using.

    1. Cross-Client Rendering: Use a tool like Litmus or Email on Acid to preview your template across dozens of clients. You’d be amazed how different an email can look in Outlook versus Gmail on an Android phone.
    2. Link Validation: Click every single link. Seriously, every one. Make sure they all lead to the correct, secure (https://) page. Nothing kills trust faster than a broken or insecure link.
    3. Image Loading: Double-check that all your images load and, just as importantly, that the alt text shows up when images are blocked by the email client.
    4. Plain-Text Version Review: Don't forget the plain-text fallback! Open it up and make sure it’s clean, readable, and includes all the essential information and links.
    5. Mobile Responsiveness: Drag your browser window to be narrow, or better yet, use a mobile simulator. Does your responsive design kick in correctly? Do the buttons stack properly?

    The diagram below breaks down the fundamental process for creating secure HTML in the first place—this is the foundation for any template that will pass these tests.
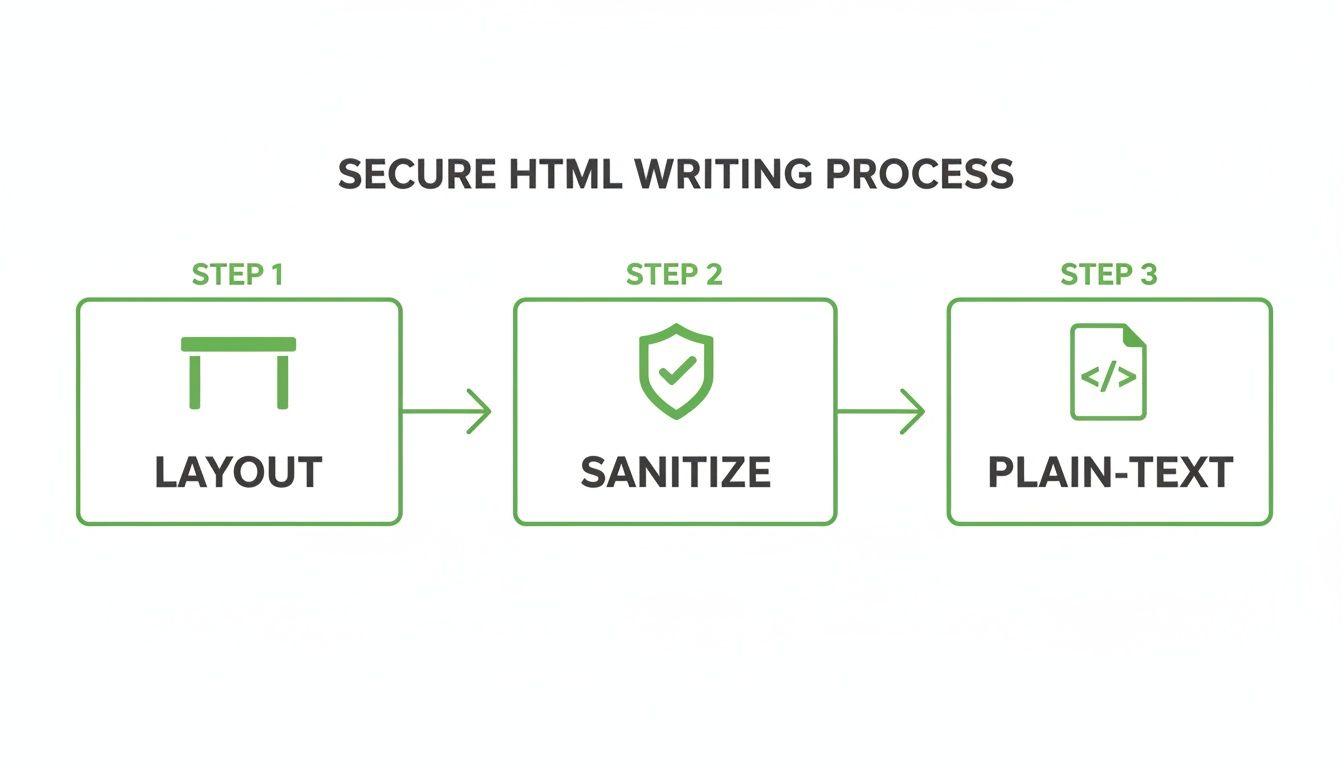
    A diagram illustrates the secure HTML writing process in three steps: Layout, Sanitize, and Plain-Text.

    This three-step flow—structuring with tables, sanitizing inputs, and always providing a plain-text version—is at the core of building a secure and universally compatible email.

    Security-Specific Audits

    Now it’s time to put on your white hat and actively search for vulnerabilities.

    • Check for Open Redirects: Make sure none of your links can be tricked into redirecting users to a malicious website. This is a classic phishing tactic.
    • Test Personalization Tokens: Send tests with both placeholder data and real data. You need to be 100% certain that your personalization logic works and will never, ever expose one user's private information to another.
    • Scan for Mixed Content: Every single asset in your email—images, web fonts, CSS files—must be loaded over HTTPS. Mixed content triggers security warnings in browsers and is a major red flag for privacy.

    A rigorous testing process is your final line of defense. It’s what transforms a well-designed template into a trustworthy communication tool, ensuring that what you send is exactly what your audience safely receives.

    Managing Templates Securely on a Platform

    Once your template aces all its tests, a hosted platform gives you the tools to manage and deploy it securely. This is about so much more than just a folder to store HTML files. For any business serious about security, it’s worth looking into the top hosted email platforms for business security to find the right fit.

    Platforms like Typewire let you set up custom sending domains, which is essential for brand recognition and deliverability. But just as important are the user permissions. You can control exactly who on your team can create, edit, or send campaigns. This creates a secure workflow that prevents costly mistakes, accidental sends, or unauthorized changes, protecting the integrity of your email program for the long haul.

    Getting the Most Out of Your Templates (And Keeping Them Secure)

    You’ve designed, built, and tested your email template. The hard part is over, right? Not quite. Now the real work begins: turning that template into a secure, profitable, long-term asset.

    A great template isn’t a "set it and forget it" project. It’s a living tool that needs to adapt over time while protecting both your audience and your brand. This is where we move past the initial setup and into the strategies that drive real, ongoing success with a focus on privacy and security.

    The goal is to build a communication channel that’s not just effective but also deeply trusted by your subscribers.

    Think in Systems, Not Files: The Modular Approach

    A single, monolithic email template is a ticking time bomb. Every time you need to update a promo banner, change a footer link, or add a new social media icon, you’re performing open-heart surgery on your code. It’s risky and inefficient.

    This is why experienced teams swear by a modular template system, often managed within a secure hosted platform. Think of it like building with LEGOs. Instead of one giant, unchangeable block, you have a library of reusable components: headers, footers, product blocks, CTA sections. You just mix and match what you need.

    Adopting this mindset has massive security and privacy payoffs:

    • Safer Updates: Need to change that privacy policy link in the footer? You edit the footer module once, and the change instantly and safely applies to every template using it. This alone slashes the risk of human error.
    • Rock-Solid Brand Consistency: A modular system is your best defense against brand drift. Every email sent from your organization will have the same polished look and feel, which is crucial for building user trust and preventing phishing confusion.
    • Launch Campaigns Faster: Assembling a new email becomes as simple as picking the right blocks. Your team can stop fighting with code and start focusing on crafting a compelling, secure message.

    Handling Dynamic Content Without Opening Security Holes

    Personalization is a game-changer for engagement. Adding a user's name or their recent order details can make an email feel much more relevant. But if you're not careful, it can also create severe privacy and security vulnerabilities.

    The key is to properly sanitize any dynamic content before it ever touches your template. A common mistake is failing to escape special characters in user-provided data. This could allow a bad actor to inject malicious code (XSS) that gets rendered in another user's email client, potentially stealing their data.

    While a good hosted email platform often handles this for you, it's critical to understand the principle: never implicitly trust user data.

    A secure template is built defensively. It assumes any piece of dynamic content could be malicious and neutralizes it before it gets rendered. This turns a potential vulnerability into a harmless string of text and protects user privacy.

    The Direct Line Between Security and Your Bottom Line

    The decisions you make about email security and privacy aren't just technical details—they have a direct, measurable impact on revenue. Strong deliverability, high engagement, and user trust are the engines of a profitable email program.

    When people trust your emails, they open them, click the links, and buy your products. Following strong email deliverability best practices, which are rooted in security fundamentals like authentication, is the first step to making sure your beautifully crafted templates even get a chance to be seen.

    The numbers don't lie. Email marketing continues to offer one of the highest returns on investment available. For 2025, the average ROI for marketing emails is a staggering 3600% to 3800%—that's about $36 in return for every dollar spent. In e-commerce, it can be even higher, sometimes hitting an astonishing 7200%, driven largely by automated and personalized templates.

    These figures prove that a secure, user-focused template isn't an expense. It's one of the most profitable investments you can make in building a trustworthy brand. For more stats, you can dig into the latest email marketing ROI insights on Designmodo.

    Common Questions About Secure Email Templates

    When you start building email templates, a lot of questions come up—especially around security and privacy. And honestly, getting these details right is what separates an email that builds trust from one that gets ignored or, worse, flagged as spam. Let's walk through some of the most common challenges I see people face and how to solve them.

    How Can I Keep My Email Templates Out of the Spam Folder?

    Avoiding the spam folder isn't about one single trick; it’s a combination of technical hygiene, smart content, and clean, secure design. From a technical standpoint, authenticating your sending domain with SPF, DKIM, and DMARC isn't optional. Think of it as the foundation of trust for every inbox provider out there.

    The template's code itself plays a huge role. Stick to clean, semantic HTML and avoid scripts or suspicious code. Steer clear of spam-trigger words like "free" or "act now," especially in your subject lines. Try to maintain a healthy text-to-image ratio, and always, always include alt text for your images. But the most powerful signal you can send is high engagement—so focus on sending valuable content people actually want.

    And one last thing: make your unsubscribe link obvious and easy to find. Hiding it is a fast track to a damaged sender reputation and privacy law violations.

    What Are the Biggest Security Risks When Creating Email Templates?

    The main security risks really come down to exposing data or creating vulnerabilities that can be exploited. One of the scariest is mishandling personalization tokens, which could accidentally leak one user's private information to another. Another big one is using unvalidated external links, which can open the door to phishing attacks or open redirect vulnerabilities.

    You also have to think about where your assets are coming from. Loading external content like images or fonts from insecure (http://) servers can create privacy issues by leaking user IP addresses to third parties and triggering browser security warnings. And if your template ever pulls in user-generated content, failing to sanitize it properly could lead to cross-site scripting (XSS) attacks in some web-based email clients.

    The single most effective way to sidestep these risks is to use a secure, hosted email platform. These services are built from the ground up to handle these issues by managing assets securely, sanitizing dynamic content, and enforcing security protocols automatically.

    Why Is a Plain-Text Version of My Email So Important?

    This one is crucial. Including a plain-text version of your email alongside the HTML isn't just a "nice-to-have." It is a fundamental aspect of secure and accessible email design.

    First, it’s all about accessibility. Screen readers, which are essential for users with visual impairments, can parse and read plain-text emails far more reliably than they can navigate complex HTML.

    Second, it has a direct impact on deliverability. Spam filters often get suspicious of emails that are only HTML, as it's a classic spammer tactic. Providing a plain-text alternative is a strong signal that you're a legitimate sender.

    Finally, it’s a matter of user preference and security. Some people, and many corporate email clients, are set up to block HTML emails by default to avoid security threats like malicious code or tracking pixels. A plain-text version guarantees your message still gets through legibly, respecting the recipient's privacy and security settings.

    How Do Hosted Platforms Make Email Templates More Secure?

    A good hosted email platform provides a managed, secure environment that takes a lot of the technical headaches and security burdens off your plate. They are specifically built to handle sending infrastructure, which means high deliverability and compliance with all the critical authentication standards.

    When it comes to your templates, these platforms offer several layers of protection:

    • Built-in sanitation for any dynamic content you use, which slashes the risk of injection attacks and data leakage.
    • Secure asset management, hosting your images and forcing HTTPS on all links to protect user data as it travels across the internet.
    • Centralized user management and access controls, so you can decide exactly who on your team can create, edit, or send emails, preventing unauthorized changes.

    This kind of centralized workflow is worlds more secure than passing HTML files around and sending from a local server. It creates a controlled process that prevents unauthorized changes and keeps your communications locked down.


    Ready to build secure, trustworthy email communications on a platform designed for privacy? Typewire provides the secure hosting, custom domains, and user management tools you need to send with confidence.
    Start your free 7-day trial of Typewire today!

  • 10 Secure Email Communication Best Practices for 2025

    10 Secure Email Communication Best Practices for 2025

    In an environment where data breaches are common and invasive tracking is the norm, standard email has become a significant liability. Your inbox, once a simple communication tool, is now a primary target for sophisticated phishing attacks, intrusive advertising, and relentless data mining. Treating it with a casual, outdated approach is no longer a viable option. Effective and professional correspondence now depends entirely on a foundation of robust security and uncompromising privacy.

    This guide moves past generic advice to provide a comprehensive roundup of essential email communication best practices designed for the modern, privacy-conscious user. We will provide actionable steps that transform your email from a point of vulnerability into a secure, efficient, and reliable asset. The focus is squarely on practical implementation, covering everything from foundational security protocols like SPF and DKIM to advanced strategies for inbox organization and user management within a secure ecosystem.

    You will learn how to leverage hosted email platforms to enforce strong privacy controls, enhance message deliverability to avoid spam filters, and master the art of secure, professional correspondence. For individuals and businesses committed to protecting their data, especially those using privacy-first services like Typewire, these practices are not just helpful tips. They represent a fundamental framework for building trustworthy, confidential, and effective communication channels. Each point in this listicle is crafted to be immediately applicable, helping you secure your digital conversations and reclaim control over your inbox.

    1. Master Hosted Email Platforms for Ultimate Control

    The single most impactful step in establishing secure and private email communication best practices is moving away from free, ad-supported services. Choosing a premium hosted email platform places you in complete control of your data, establishing a secure foundation for all other privacy measures. Unlike free services that often treat your data as the product through tracking and ad-targeting, a hosted platform operates on private infrastructure dedicated to protecting your information.

    Why Hosted Email is Non-Negotiable for Privacy

    A hosted email solution means your communications are not scanned to build advertising profiles or sold to data brokers. This model is fundamentally aligned with user privacy. The provider’s business is to protect your data, not monetize it. This separation is critical for maintaining confidentiality and security, especially when handling sensitive information.

    For example, a law firm using a platform like Typewire can guarantee attorney-client privilege, as communications are stored on secure, private servers inaccessible to third parties. Similarly, a healthcare provider can manage patient correspondence in a HIPAA-compliant environment, a feat nearly impossible with standard free email accounts.

    Key Insight: With a hosted email platform, you are the customer, not the product. Your privacy is a feature you pay for, not a commodity to be traded.

    Actionable Steps for Implementation

    Making the switch to a hosted platform is straightforward. Follow these tips to ensure a successful transition and maximize your control:

    • Prioritize Full-Stack Providers: Select a provider that owns and operates its own hardware and data centers, like Typewire. This model eliminates the risks associated with third-party data handlers and gives you a single point of accountability for security.
    • Leverage User Management Tools: Once set up, use the platform's administrative controls to create custom roles and permissions for your team. This ensures that employees only access the information necessary for their jobs, minimizing internal data exposure.
    • Utilize Free Trials: Before committing, take advantage of trial periods to test the platform’s security features, user interface, and overall performance. Confirm it meets your specific workflow and compliance needs.
    • Confirm 24/7 Support: Ensure your chosen provider offers robust, around-the-clock support. Immediate access to expert help is crucial for resolving any potential security or deliverability issues.

    2. Personalize Email Content Without Sacrificing Privacy

    True personalization in email communication best practices goes far beyond a simple [First Name] merge tag. It involves creating a tailored experience by leveraging recipient-specific information, but it must be done within a secure, privacy-first framework. This dynamic approach transforms generic broadcasts into relevant, one-to-one conversations that build trust, all while respecting user privacy and avoiding invasive data collection.

    An iPad displaying a webpage with 'Beyond Names' and 'consgam' logo, showing various profile pictures.

    Why Advanced Personalization is a Privacy-First Strategy

    When executed responsibly, advanced personalization strengthens the user relationship because it is based on consent and delivered value. Unlike invasive tracking, this strategy relies on voluntarily provided or first-party engagement data to enhance the user experience, not exploit it for third-party advertising. The goal is to deliver content so relevant that it feels like a service, not a sales pitch, all within the secure confines of your hosted email platform.

    For example, a project management tool might send a user an email with tips specifically for a feature they frequently use, enhancing their workflow. A privacy-focused platform like Typewire could use onboarding data to send customized security checklists, helping new teams configure their accounts for maximum protection from day one. This level of detail demonstrates that you understand and respect the user’s needs without compromising their data.

    Key Insight: Meaningful personalization is a sign of respect for your audience's time and privacy. It proves you are listening and shifts your communication from being intrusive to being indispensable.

    Actionable Steps for Implementation

    Implementing advanced personalization requires a strategic approach that prioritizes data privacy and relevance. Follow these steps to create emails that resonate deeply with your audience:

    • Segment Audiences Meaningfully: Move beyond basic demographics. Create segments based on engagement levels (e.g., active users, inactive users), feature usage, or content preferences to send highly targeted messages.
    • Utilize Dynamic Content: Implement conditional content blocks within your emails. This allows you to show or hide specific sections based on a recipient's segment, so a single campaign can deliver multiple personalized versions.
    • Implement Progressive Profiling: Use forms to gradually collect more information over time instead of asking for everything at once. This builds a richer user profile in a non-intrusive way, respecting the user's comfort level.
    • Prioritize Consent and Transparency: Always be clear about what data you are collecting and how it will be used to personalize their experience. Provide easy-to-find opt-out options for all types of communication.

    3. Maintain Consistent Sending to Boost Sender Reputation

    Establishing a predictable sending schedule is a core component of effective email communication best practices, building trust with both your audience and email service providers. Irregular sending patterns, such as long periods of silence followed by a sudden burst of messages, can trigger spam filters and damage your sender reputation. A consistent cadence signals to inbox providers that you are a legitimate, reliable sender, which is crucial for email security and deliverability.

    Why Consistency Builds Trust and Deliverability

    A regular email schedule conditions your audience to expect your communications, reducing the likelihood of spam complaints. From a technical security perspective, email platforms like Typewire analyze sending volume and frequency to assess sender reputation. Consistency demonstrates responsible email behavior, preventing your messages from being flagged as suspicious or part of a potential spam attack. This is a key factor in passing through modern, AI-driven security filters.

    For example, a security-focused newsletter arriving at the same time each week builds a powerful reader habit and reinforces its legitimacy. This predictability helps email servers differentiate your planned communications from anomalous, potentially malicious activity, ensuring your important security updates or account notifications are not mistakenly filtered.

    Key Insight: Consistency is not just about marketing; it’s a security and deliverability signal. Predictable sending patterns are a hallmark of a trustworthy sender, reducing the risk of being flagged by spam filters.

    Actionable Steps for Implementation

    Creating a reliable schedule is a strategic process that enhances your security posture. Use these steps to build a consistent and effective sending rhythm:

    • Analyze Engagement Metrics: Dive into your email analytics to identify the days and times when your audience is most active. Use this data to establish a baseline for your sending schedule, optimizing for secure and reliable delivery.
    • Create an Editorial Calendar: Plan your content in advance. An editorial calendar removes the pressure of last-minute content creation and ensures a steady, predictable stream of communication that email servers recognize as legitimate.
    • Offer Frequency Preferences: Empower your subscribers by allowing them to choose how often they hear from you (e.g., daily, weekly, or monthly). This respects user preference and reduces the chance of spam complaints that harm your reputation.
    • Secure Your Foundation: Ensure your scheduling efforts are supported by robust security. For a comprehensive approach to securing your digital identities, refer to these credential management best practices for secure accounts.

    4. Implement Clear Call-to-Action (CTA) Buttons to Prevent Phishing

    Effective email communication guides the recipient toward a specific, safe action. Implementing prominent, unambiguous call-to-action (CTA) buttons is a critical component of secure email communication best practices. Clear CTAs provide a trusted, low-friction path for your audience, helping them distinguish legitimate requests from the deceptive links often found in phishing attacks.

    Close-up of a smartphone displaying an email with a 'Call To action' message on a wooden table.

    Why Clear CTAs Enhance Security

    In an era of sophisticated phishing, a well-designed CTA builds user confidence. When your emails consistently use a clear, branded button for primary actions, users learn to recognize it as a legitimate signal. This makes them less likely to click on rogue text links or suspicious attachments. A clear CTA removes ambiguity and trains recipients to look for trusted visual cues before acting, reinforcing secure online behavior.

    For example, a bank that always uses a distinct, blue 'Login to Your Account' button trains its customers to be wary of emails that use generic text links for the same action. This simple design consistency becomes a subtle but powerful security feature, helping users spot fraudulent attempts to steal their credentials.

    Key Insight: A call-to-action button is not just a link; it's a visual and psychological cue that directs user behavior and can be a key part of your anti-phishing strategy.

    Actionable Steps for Implementation

    Creating high-performing, secure CTAs involves a blend of design principles and strategic placement. Use these tips to craft buttons that get results:

    • Use First-Person Action Verbs: Frame the CTA from the user’s perspective to create a sense of ownership. Text like 'Access My Secure Portal' or 'Verify My Account' clearly communicates the action and intent.
    • Ensure Mobile Accessibility: Design buttons with a minimum height of 40-60 pixels to make them easy to tap on mobile devices. A frustrating mobile experience can lead users to seek alternative, less secure methods.
    • Prioritize Color Contrast: To meet accessibility standards and ensure visibility, aim for a color contrast ratio of at least 4.5:1 between the button and its background. Use a prominent, on-brand color that stands out.
    • Place CTAs Strategically: Position your primary CTA "above the fold" so it is visible without scrolling. Ensure the destination URL is clear and directs to your secure, HTTPS-enabled domain.

    5. Optimize Email Layout for a Secure Mobile Experience

    With over half of all emails now opened on mobile devices, optimizing your layout for smaller screens is a core tenet of secure email communication best practices. A mobile-first approach ensures your messages are readable and professional, but more importantly, it helps prevent user error that can lead to security risks. A poorly rendered email can cause users to misclick on malicious links or struggle to identify legitimate sender details.

    A person holds a smartphone displaying a webpage titled 'Mobile Optimized' with text, outdoors.

    Why Mobile-First Design is Crucial for Security

    A responsive email design automatically adapts its layout to fit the screen, ensuring a seamless and secure experience. When an email is difficult to read, users may rush through it, missing subtle signs of a phishing attempt. Clear, legible text and properly sized buttons reduce the chance of accidental clicks on malicious content disguised to look like legitimate links.

    For instance, a responsive design ensures that the sender's email address is fully visible, not truncated, allowing the recipient to verify its authenticity. For internal communications on a secure platform like Typewire, a responsive layout ensures that team members on the go can quickly read and act on important security alerts without the risk of misinterpretation caused by a broken layout.

    Key Insight: Mobile optimization is a security feature. A clean, responsive design reduces user error and makes it easier for recipients to identify and avoid phishing threats.

    Actionable Steps for Implementation

    Ensuring your emails are secure and readable on every device is a technical but achievable goal. Use these strategies to create a consistently safe viewing experience:

    • Adopt a Single-Column Layout: Use a single-column structure that stacks content vertically. This is the most reliable way to ensure readability and prevent elements from overlapping or becoming unclickable on narrow screens.
    • Utilize CSS Media Queries: Implement media queries in your email’s code to apply different styles based on screen width. This allows you to adjust font sizes and reformat layouts to maintain clarity on mobile devices.
    • Compress Images: Large image files can slow down loading times, especially on mobile data connections. Compress all images to ensure the email loads quickly and completely.
    • Test Extensively: Before sending, use tools to preview your email across dozens of mobile clients and devices. This helps you confirm that all links are correctly rendered and that there are no layout issues that could obscure important security information.

    6. Build and Maintain a Clean Email List for Security

    A core component of effective email communication best practices involves prioritizing list quality over quantity. Maintaining a clean email list is not just about deliverability; it's a security and privacy fundamental. A bloated list filled with inactive, invalid, or disengaged subscribers increases your risk profile, wastes resources, and damages your sender reputation, making it harder for your legitimate communications to reach their intended recipients.

    Why List Hygiene is a Security Imperative

    A clean, engaged email list is a direct reflection of a healthy sender reputation. Internet Service Providers (ISPs) and secure email platforms like Typewire analyze engagement metrics to filter spam and malicious content. High bounce rates from sending to non-existent addresses can signal that your system may be compromised and used for spamming. This hygiene practice ensures your critical communications are not mistakenly flagged as threats.

    For instance, a financial services firm sending quarterly statements must ensure its list is pristine. Removing hard bounces immediately prevents repeated attempts to send sensitive information to non-existent or compromised addresses, closing a potential security loophole. Regularly purging unengaged users also reduces the data footprint, minimizing the impact of a potential data breach.

    Key Insight: A clean email list is your first line of defense in protecting sender reputation. It tells receiving servers that you are a legitimate, responsible communicator, ensuring critical emails are delivered securely.

    Actionable Steps for Implementation

    Implementing a consistent list hygiene strategy is crucial for maintaining both deliverability and security. Follow these steps to build and maintain a high-quality email list:

    • Implement Double Opt-In: Require new subscribers to confirm their email address via a confirmation link. This validates every address from the start and prevents malicious bots from flooding your list with fake accounts.
    • Remove Hard Bounces Immediately: Configure your sending platform to automatically remove email addresses that result in a hard bounce (a permanent delivery failure). This is a critical signal to ISPs that you manage your list responsibly.
    • Create Re-Engagement Campaigns: For subscribers who have been inactive for a set period, such as 90 days, launch an automated re-engagement campaign. If they do not interact, remove them from your active sending list to reduce your attack surface.
    • Monitor Spam Complaint Rates: Pay close attention to your spam complaint rate. Immediately remove any user who marks your email as spam to prevent further damage to your domain’s reputation.

    7. Use Authentication Protocols (SPF, DKIM, DMARC)

    Implementing modern email authentication protocols is a non-negotiable step for establishing trust and security. Standards like SPF, DKIM, and DMARC are technical safeguards that verify a sender's identity, effectively preventing domain spoofing and phishing attacks. These protocols are the bedrock of secure email communication best practices, as they signal to receiving mail servers that your messages are legitimate and trustworthy.

    Why Authentication is Critical for Security and Deliverability

    Email authentication acts as a digital passport for your domain, confirming to providers like Gmail and Microsoft that messages sent from your address are authorized. Without these records, your emails can be easily impersonated by malicious actors who can send phishing emails from your domain. A strong DMARC policy tells receiving servers to reject such fraudulent emails, protecting your brand reputation and your customers.

    For instance, after implementing a strict DMARC policy, a financial services firm can prevent scammers from sending fraudulent invoices using its domain, protecting both its reputation and its clients. This is a foundational security measure for any organization. Learn more about how these protocols work together in our complete security guide to email authentication.

    Key Insight: Email authentication transforms your domain's reputation from a question mark into an undeniable statement of legitimacy, directly improving security and deliverability.

    Actionable Steps for Implementation

    Configuring these protocols involves adding specific DNS records for your domain. Here’s how to get started:

    • Start with an SPF Record: Create a TXT record in your DNS settings that lists all authorized mail servers for your domain. This tells receiving servers which IP addresses are permitted to send email on your behalf.
    • Implement DKIM Signing: Enable DKIM within your email provider’s settings, like Typewire. This adds a unique digital signature to your emails, which receiving servers can verify using a public key published in your DNS.
    • Deploy DMARC Gradually: Begin with a monitoring-only policy (p=none). This allows you to receive reports on who is sending email from your domain without affecting mail flow.
    • Enforce Your DMARC Policy: Once you confirm all legitimate mail is authenticated, move to a p=quarantine policy to send unverified emails to spam, and finally to p=reject to block them entirely.

    8. Segment Email Lists for Privacy and Relevance

    Sending generic, one-size-fits-all emails is one of the fastest ways to land in the spam folder. A core component of modern email communication best practices is segmentation—dividing subscribers into smaller groups. From a privacy perspective, this ensures you only send information relevant to a specific user group, adhering to the principle of data minimization and purpose limitation.

    Why Segmentation is Crucial for Privacy and Security

    Segmentation moves your email strategy from a broadcast to a secure, targeted conversation. Instead of sending sensitive information to your entire list, you can restrict it to only the relevant audience, reducing the risk of accidental data exposure. This targeted approach minimizes the likelihood of users marking your emails as spam, which is vital for maintaining a strong sender reputation.

    For example, a SaaS company using a secure platform like Typewire can segment its users by account type. An email containing a security update relevant only to enterprise customers can be sent exclusively to that segment, preventing unnecessary notifications and potential confusion for other users. This ensures every communication is valuable and respects the recipient's context, reinforcing trust.

    Key Insight: Segmentation is a privacy-enhancing tool. Sending relevant content reduces data exposure, builds trust, and protects your sender reputation.

    Actionable Steps for Implementation

    Implementing a powerful segmentation strategy is more accessible than it seems. Start with a few core groups and expand as you gather more data.

    • Define Foundational Segments: Begin by grouping your audience based on clear, consent-based criteria. Common starting points include new subscribers (for welcome series) or product usage levels (for feature updates).
    • Use Behavioral Triggers: Set up automated campaigns based on user actions within your application. Send a security tip to a user who just enabled a new feature. This real-time relevance is highly effective.
    • Combine Criteria for Micro-Targeting: Create granular segments by combining multiple data points. For instance, target "administrators of enterprise accounts" for a specific security policy update.
    • Regularly Clean Your Lists: Create a segment of inactive or unengaged subscribers. Send them a re-engagement campaign and remove those who don’t respond to keep your list healthy and minimize your data footprint.

    9. Create Valuable Content that Reinforces Security

    One of the most powerful email communication best practices involves shifting your focus from selling to serving, particularly by providing content that reinforces security and privacy awareness. Instead of sending purely promotional messages, you build trust by offering genuine value that also helps protect your users. This approach transforms your email into a welcome resource that strengthens your security posture.

    Why Value-Driven Content Enhances Security

    A value-first content strategy respects your subscribers' time and reinforces your commitment to their privacy and security. When your audience expects helpful security tips or privacy updates, they are more likely to engage with your messages and trust your brand. This positive engagement improves your sender reputation and ensures critical communications reliably reach the inbox.

    For instance, a cybersecurity firm could send a weekly digest of emerging threats and protection tips, establishing itself as a trusted authority. Similarly, a hosted email provider like Typewire can educate users on enabling two-factor authentication or recognizing phishing attempts. This content model provides tangible value while actively contributing to a more secure ecosystem for your users.

    Key Insight: Treat your subscribers' inbox as a privileged space. Earning your place there requires consistently delivering content that solves their problems, educates them, and helps keep them safe.

    Actionable Steps for Implementation

    Creating valuable, security-focused content is a systematic process. Use these tips to build a content strategy that serves your audience and strengthens your brand:

    • Follow the 80/20 Rule: Dedicate 80% of your content to providing value—security education, privacy insights, or best practice guides—and reserve only 20% for direct promotional messages.
    • Share Original Security Insights: Develop and distribute unique content like case studies on resolved security incidents (anonymized) or data-driven analyses of phishing trends.
    • Tell Authentic Stories: Share lessons learned about security challenges and successes. Authentic storytelling builds a human connection and makes your security advice more relatable.
    • Create Educational Content: Develop an email series that teaches users how to use your platform's security features. To streamline your messaging, explore these effective business email templates to structure your communications clearly.

    10. Monitor Key Email Metrics and Continuously Test

    To master a secure communication strategy, you must analyze performance. Monitoring key metrics and continuously testing different elements are essential email communication best practices that transform guesswork into a data-driven process. This allows you to systematically improve engagement and deliverability without compromising user privacy.

    Why Data-Driven Optimization is a Privacy-Conscious Approach

    A data-driven approach ensures your communication efforts are not wasted. By tracking metrics like open rates, click-through rates, and bounce rates within your own platform, you gain direct insight into audience behavior without sharing data with third-party trackers. Unlike ad-based platforms that track users across the web, your internal analytics focus solely on improving communication effectiveness within your secure environment.

    For instance, A/B testing a subject line about a new security feature can reveal which wording encourages more users to adopt it. Analyzing bounce rates can help you identify list hygiene issues before they damage your sender reputation. A hosted platform like Typewire provides these analytics in a private environment, ensuring your optimization efforts do not come at the cost of user privacy.

    Key Insight: Data-driven testing provides empirical evidence of what works. It replaces assumptions with facts, allowing you to optimize every element of your email for maximum impact and security.

    Actionable Steps for Implementation

    Implementing a testing framework is a powerful way to enhance your email strategy. Use these steps to build a continuous improvement cycle:

    • Isolate a Single Variable: To get clear results, test only one element at a time (A/B testing). For example, test two different subject lines while keeping the email body and send time identical.
    • Ensure Statistical Significance: Test with a large enough sample size to ensure your results are reliable. Most secure email platforms can help you determine the right audience size.
    • Track Key Performance Indicators (KPIs): Monitor core metrics such as open rate and click-through rate (CTR). Also, track negative security indicators like hard bounces and spam complaints, which are critical for maintaining a healthy sender reputation. For a deeper dive, learn more about email deliverability best practices on typewire.com.
    • Document and Iterate: Keep a record of your hypotheses, test results, and key learnings. This documentation becomes an invaluable playbook for creating more effective and secure email communications in the future.

    10-Point Email Best Practices Comparison

    Strategy 🔄 Implementation Complexity ⚡ Resource Requirements 📊 Expected Outcomes 💡 Ideal Use Cases ⭐ Key Advantages
    Craft Clear and Compelling Subject Lines Low — copywriting + A/B testing Low — writer time, testing tool Higher open rates; improved engagement Announcements, promos, newsletters Fast, measurable lift in opens
    Personalize Email Content Beyond Name Insertion High — data integration & dynamic logic High — CRM/MA platform, data ops, privacy controls Higher CTRs, conversion, LTV lift E‑commerce, SaaS lifecycle, retention Greatly increases relevance and revenue
    Maintain Consistent Email Sending Schedule Medium — editorial planning & cadence control Medium — scheduling tools, content pipeline Better deliverability; predictable engagement Newsletters, daily/weekly digests, drip series Builds trust and reduces spam flags
    Implement Clear Call-to-Action (CTA) Buttons Low–Medium — design + cross-client QA Low — design assets, QA across clients Higher click-through and conversion rates Promotional offers, onboarding, product pages Directs user action; reduces friction
    Optimize Email Layout for Mobile Devices High — responsive coding & extensive testing Medium–High — developers, builders, testing tools Improved mobile engagement and conversions Mobile-first audiences, B2C, retail Improves usability and accessibility on devices
    Build and Maintain a Clean Email List Medium — ongoing hygiene processes Medium — validation tools, re-engagement workflows Better deliverability; lower costs; accurate metrics Any sender prioritizing deliverability Protects sender reputation; increases ROI
    Use Authentication Protocols (SPF, DKIM, DMARC) High — DNS configuration + monitoring Low–Medium — IT support, monitoring tools Significantly improved deliverability and security All bulk senders; brands facing spoofing risk Prevents spoofing and improves inbox placement
    Segment Email Lists for Targeted Campaigns Medium–High — segmentation rules & maintenance Medium — analytics, automation platform Higher open/click rates; better conversions E‑commerce, SaaS, targeted promotions Enables highly relevant messaging and ROI lift
    Create Valuable Content That Serves Subscribers Medium–High — content strategy & production High — writers, designers, editorial calendar Stronger retention, shares, brand authority Thought leadership, retention-focused newsletters Builds trust and long-term engagement
    Monitor Key Email Metrics and Continuously Test Medium — analytics and test design Medium — analytics tools, testing cadence Incremental performance gains; data-driven choices Any program seeking optimization at scale Enables measurable, continual improvement

    Securing Your Digital Dialogue: The Way Forward

    Navigating the landscape of digital communication requires more than just knowing how to compose a message. It demands a deliberate, security-first mindset. Throughout this guide, we've explored a comprehensive suite of email communication best practices, moving far beyond generic advice to provide actionable strategies that fortify your digital perimeter. We've deconstructed everything from the foundational necessity of authentication protocols like SPF, DKIM, and DMARC to the privacy-enhancing benefits of list segmentation. Each practice, whether technical or strategic, serves as a crucial building block in constructing a resilient and effective email framework.

    The central theme is clear: true mastery of email communication hinges on a commitment to privacy and security. It's about recognizing that a clean email list is as vital to your security posture as a strong password policy. It’s understanding that a mobile-optimized layout isn't just about aesthetics; it's about preventing user error that can lead to security breaches. These are not isolated tasks to check off a list but interconnected components of a holistic communication strategy built on a secure, hosted email platform.

    From Theory to Action: Your Next Steps

    The value of these principles lies in their application. Merely understanding the importance of DMARC or list segmentation is not enough. The real transformation begins when you translate this knowledge into tangible action. Your immediate priority should be to conduct a thorough audit of your current email practices against the security and privacy benchmarks outlined in this article.

    Here is a simple, actionable plan to get you started:

    • Technical Audit: Begin with the non-negotiables. Verify your domain’s SPF, DKIM, and DMARC records immediately. These are not advanced features but the fundamental price of entry for secure, deliverable email in the modern era. Use online tools to check your configuration and address any gaps.
    • Platform Review: If you are not already using a hosted email platform, evaluate your options. Prioritize providers that offer end-to-end encryption, own their infrastructure, and have a clear, privacy-focused business model.
    • List Hygiene Protocol: Commit to a regular schedule for cleaning your email list. Don't wait until your bounce rates skyrocket. Establish a process for removing inactive subscribers and verifying new ones to maintain both high deliverability and compliance with privacy standards.

    The Lasting Impact of a Security-First Approach

    Adopting these email communication best practices yields benefits that extend far beyond improved open rates. When you prioritize security and privacy, you build trust. Your subscribers, clients, and team members learn that communication from you is legitimate, safe, and respectful of their data. This trust is the bedrock of strong professional relationships and a reputable brand identity.

    By embracing a secure, hosted email platform as your foundation, you empower yourself to implement these practices effectively. You move away from consumer-grade services that mine your data and into an environment where you control the security settings, manage users with precision, and communicate with the confidence that your conversations remain private. This isn't just about sending better emails; it's about building a better, more secure, and more professional way to communicate. The journey requires commitment, but the rewards of a secure, private, and powerful digital dialogue are well worth the effort.


    Ready to build your communication on a foundation of privacy and security? Typewire provides the secure, ad-free hosted email platform you need to implement these best practices with confidence. Take control of your data and elevate your professional communications by exploring our private email solutions at Typewire today.