Author: williamwhite

  • Email Bounce Explained: Soft vs Hard Bounces & How to Fix Them

    Email Bounce Explained: Soft vs Hard Bounces & How to Fix Them

    An email bounce is a returned undelivered message. Hard bounces are permanent failures, while soft bounces are temporary, and both can be fixed once you know what caused them.

    Many small business owners only notice the problem when a newsletter starts coming back with error notices. That feels like a mailing issue, but it often points to list quality, authentication, or mailbox-provider filtering. We'll keep this simple and practical, so you can read the bounce, understand what it means, and know what to do next.

    Introduction

    A bounced email is a message the receiving system sends back because it could not deliver it. A hard bounce usually means the address is invalid or permanently unreachable, while a soft bounce usually means the problem is temporary.

    That difference matters because the fix is different. If the address is dead, you remove it. If the mailbox is full or the server is busy, you retry later and watch for patterns.

    A common situation looks like this. You send a product update on Monday, the list looks healthy, and then a few replies start showing delivery errors from old contacts, mistyped addresses, or overloaded inboxes. The bounce itself is not the whole story. It is a signal about your data, your sending setup, or the recipient's mail system.

    For privacy-focused senders, the signal matters even more. Canadian-hosted mail still depends on trust, consent, and technical alignment, not just whether an address exists. A 2026 Canadian benchmark found that the average hard bounce rate was about 0.27%, yet the same report estimated that 15% to 20% of real emails never reach the inbox because they fail relevance, trust, and compliance filters (Cyberimpact 2026 State of Email Marketing in Canada Report).

    That is why this guide focuses on five practical jobs. You will learn what a bounce is, how soft and hard bounces differ, why they happen, how to read bounce-back messages, and how to cut future bounces before they hurt your reach. Bounces are diagnostic signals, not just failures.

    What is an email bounce

    Your message leaves your sending server, then the recipient's server decides what to do with it. In SMTP terms, that handoff is the normal path for email delivery. A bounce happens when the receiving server refuses the message and sends it back.

    The server can answer in only three ways. It can accept the message, refuse it, or accept it and filter it later. That last case is why people sometimes see an email “sent” even though it never reaches the inbox.

    A concrete sender scenario makes this easier to see. You send a campaign, the message reaches the recipient's server, and the server rejects it because the address does not exist, the mailbox is full, or the message fails a policy check. The bounce notice is the clue. It tells you the handoff failed.

    Bounce, block, and spam are not the same thing

    A bounce means the message was refused during delivery. A block means the receiving system chose not to accept it, often because of reputation or policy. A message that lands in spam was usually accepted first, then filtered out of the inbox.

    That difference matters because hidden deliverability loss can look healthy on the surface. As noted earlier, the Canadian benchmark showed that many messages still miss the inbox because of trust, relevance, and compliance filters, even when the sending side looks technically fine. A low bounce rate does not prove strong inbox placement.
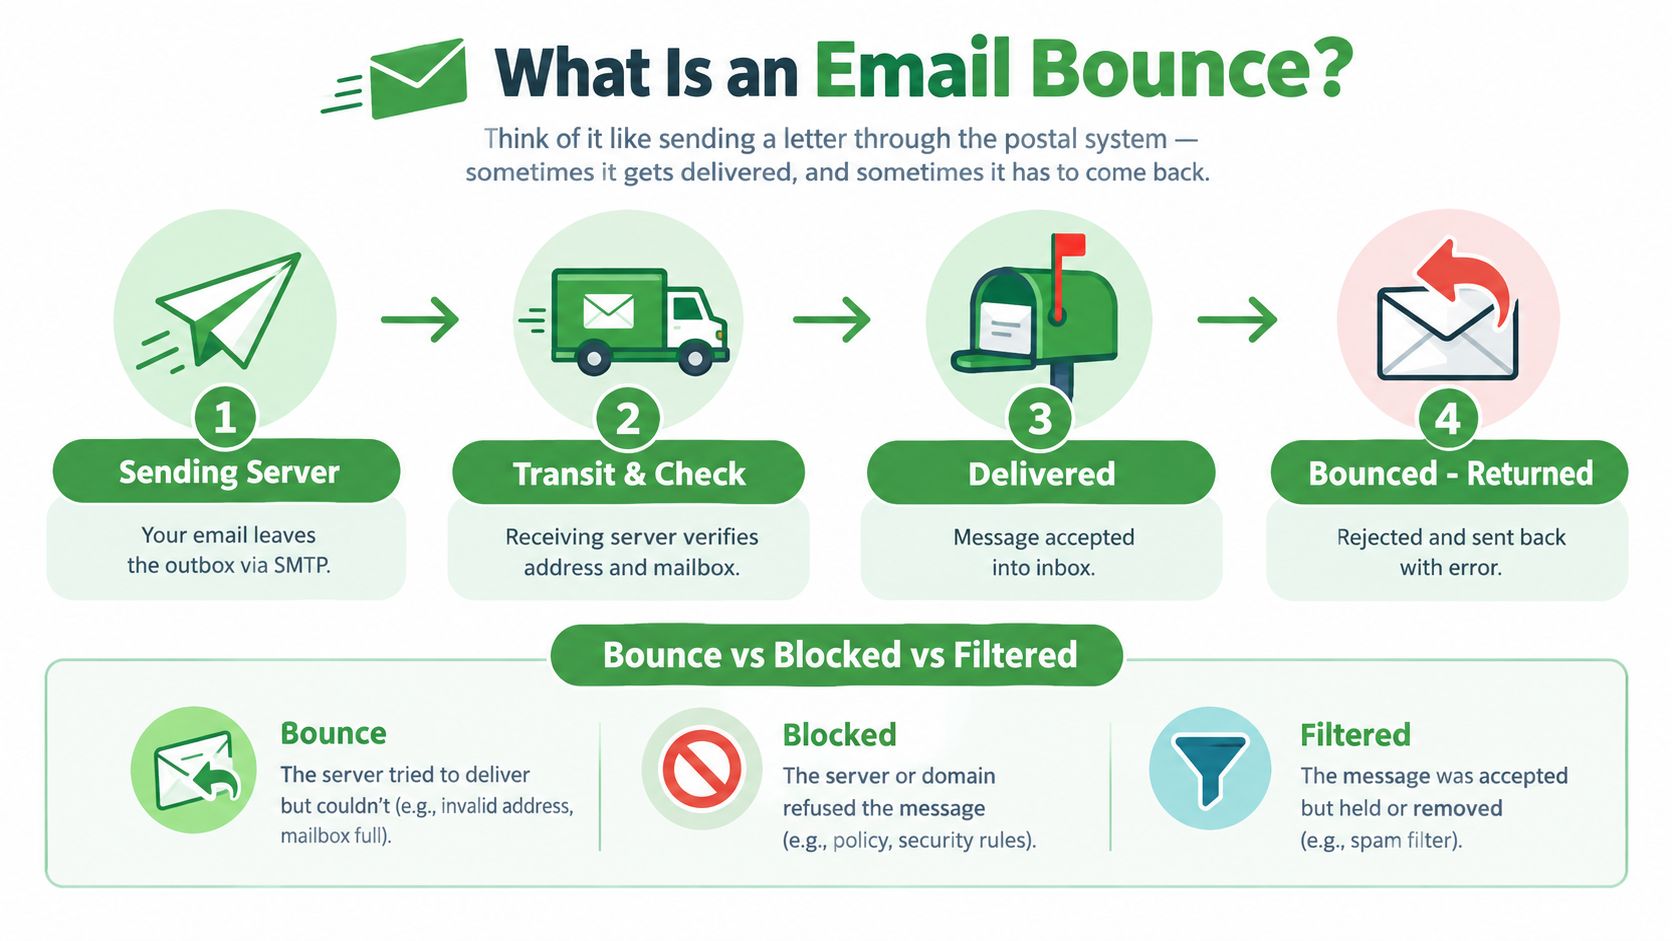
    An infographic illustration explaining the email bounce process, from sending a message to a failed delivery.

    Why bounces protect both sides

    Receiving systems use bounce logic to protect mailboxes from bad addresses, oversized messages, and suspicious traffic. Sender systems use it to avoid wasting effort on mail that will never arrive. Like a return label on a parcel, the bounce notice protects the route and shows where the delivery failed.

    For Canadian senders, that signal also connects to compliance and trust. Strong authentication, clean consent records, and accurate lists reduce the chance that a server rejects your mail before the inbox ever sees it. That is why bounce handling is part of healthy email operations, not a sign that something is always broken.

    Practical rule: if a message was never accepted, treat it as a delivery problem. If it was accepted but not seen, treat it as an inbox-placement problem.

    Once you separate those two outcomes, bounce notices become easier to read. You can tell whether you need to fix an address, retry later, or look deeper into authentication and consent.

    Soft bounce vs hard bounce

    A soft bounce is temporary. A hard bounce is permanent. The label matters, but the response matters more, because each one sends you toward a different fix and affects your sender reputation in a different way.

    Feature Hard Bounce Soft Bounce
    Meaning Permanent delivery failure Temporary delivery failure
    Common outcome Remove or suppress the address Retry later and watch for repeats
    Typical cause pattern Invalid address, bad domain, permanent rejection Full mailbox, busy server, message issue
    Risk if repeated High, because the address will not recover Medium, because repeated soft failures can become a list-quality problem
    Best action Suppress immediately Retry for a short period, then review

    A hard bounce is like a parcel returned to sender because the street number does not exist. There is no useful retry. Remove the address so future sends do not keep hitting the same dead end.

    A soft bounce is different. The mailbox may be full, the server may be busy, or the message may have hit a temporary issue. In those cases, a retry makes sense, but only for a short time.

    How to decide what to do

    If the address does not exist, stop sending to it. If the mailbox is full or the server is unavailable, give the system time to clear and try again later.

    One failed send is not the whole story. A mailbox can be full for a day, while an invalid address will stay invalid. If the same contact keeps soft-bouncing, treat it like a hard bounce in practice and suppress it.

    Why list hygiene wins here

    Hard bounces are the clearest sign of stale list data. Keeping them active adds noise to future campaigns and makes clean reporting harder. Soft bounces are more forgiving, but repeated ones still point to a list that needs attention.

    If a contact keeps failing for the same reason, stop treating it as a one-off.

    For small teams, the rule is simple. Remove hard bounces right away, retry soft bounces only for a short window, and suppress anything that keeps failing. That keeps your list cleaner and helps protect deliverability without extra complexity.

    For a quick visual walkthrough of the retry-versus-remove decision, watch this short explainer.
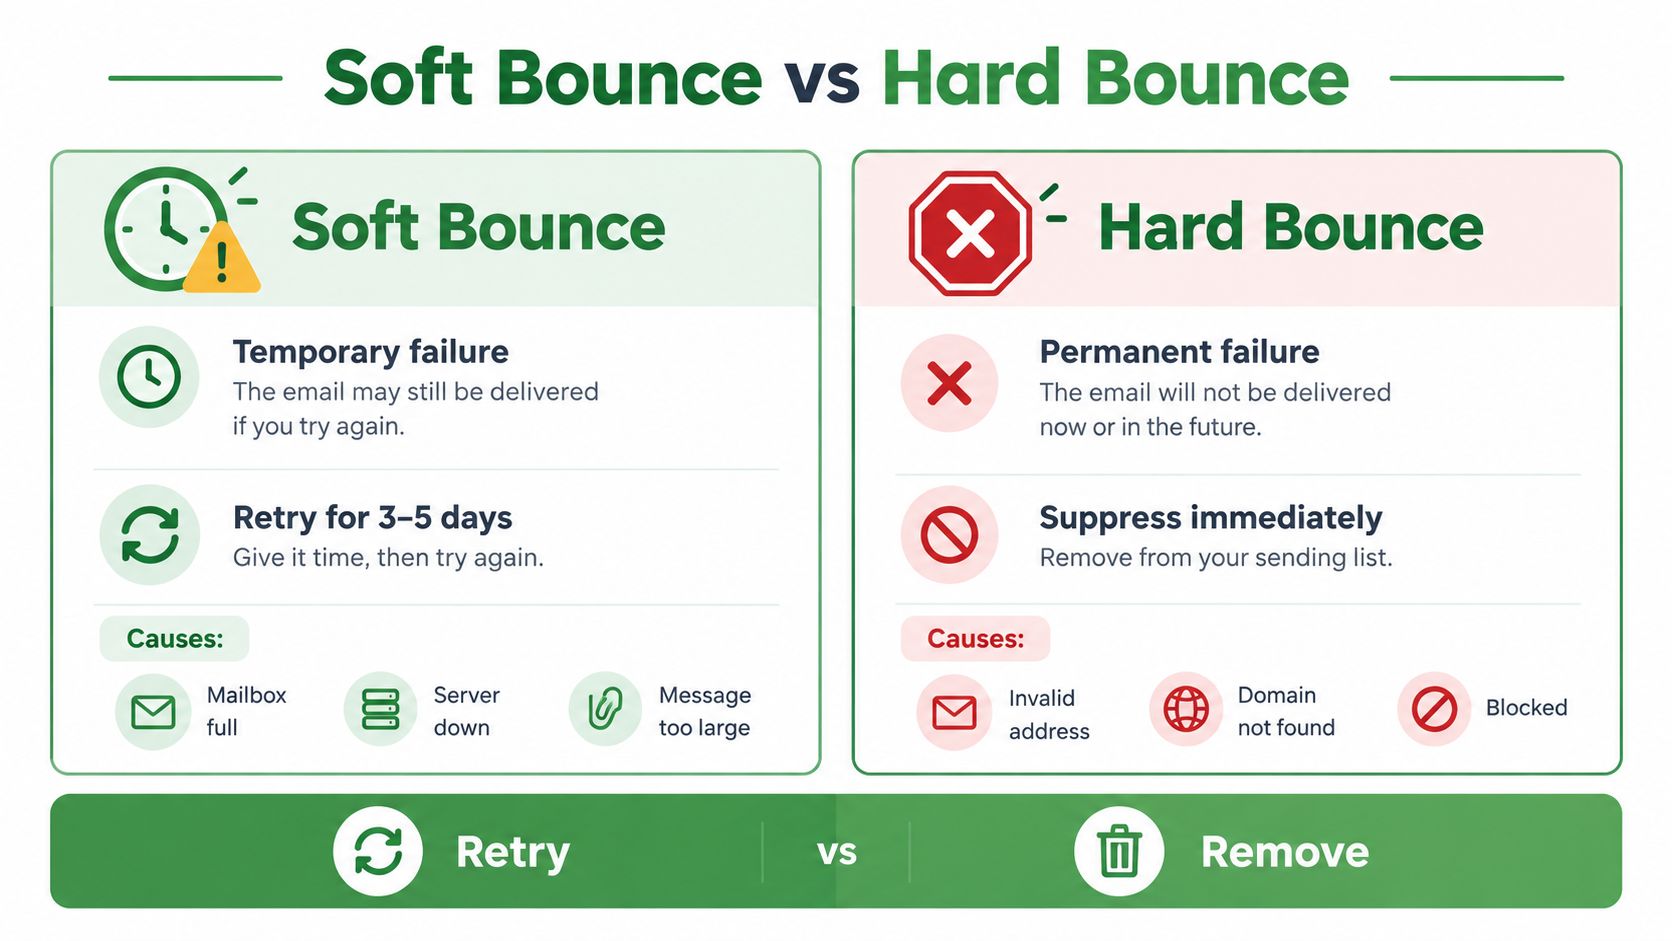
    A comparison infographic showing the differences between soft bounce and hard bounce email delivery failures.

    Common bounce reasons

    Bounce reasons usually fall into three groups, recipient-side issues, sender-side issues, and policy-side issues. That grouping helps you stop blaming the wrong thing. A full mailbox and a failed authentication check need very different fixes.

    Recipient-side problems

    The easiest case is a bad address. Someone mistyped the domain, closed the mailbox, or never had that address in the first place. A mailbox can also be full, which is temporary, but it still blocks delivery until the recipient clears space.

    These are the kinds of problems that show up when lists get old. People leave jobs, change providers, or stop checking an address they once used. If your list came from a form, a trade show, or a manual import, old data often shows up here first.

    Sender-side and policy-side problems

    Authentication failures matter too. The Canadian Centre for Cyber Security says an email can pass DMARC only if it passes SPF or DKIM, and the domain used in those checks must align with the domain in the From field. If an email fails both SPF and DKIM, it fails DMARC (Canadian Centre for Cyber Security DMARC guidance).

    That matters because some messages do not bounce for bad addresses, they bounce because the receiver does not trust the sender. Consent and list quality matter here as well, especially under CASL expectations in Canada. A list built on weak consent or stale contacts creates more delivery friction, more filtering, and more avoidable failures.

    If you want to understand whether a failure is caused by trust, domain setup, or list quality, start with the bounce wording first and the code second. The message usually points you toward the right bucket before you go deeper into logs or headers.

    A sender can waste time if they only look at one metric. A Canadian deliverability benchmark noted that roughly 15% to 20% of emails can miss the inbox, while another benchmark put Canadian bounce rate around 2.19%, so the bounce itself is only part of the failure path (Cyberimpact deliverability statistics). If you want to reduce failures properly, you need both list hygiene and trust signals.

    For setup work, this guide on SPF is useful: how to create an SPF record.

    Reading a bounce-back message

    A bounce-back message usually has three parts. The first part is a plain-language explanation. The second is an SMTP status code. The third may be a diagnostic line or server detail that explains the failure more precisely.

    The three parts that matter

    Start with the plain-language line. It might say the mailbox is full, the user does not exist, or the server is unavailable. Then check the code. That tells you whether the problem is temporary or permanent.

    4xx codes usually point to temporary failures, which fit soft bounces. 5xx codes usually point to permanent failures, which fit hard bounces. 421 often signals a temporary issue, 550 often signals a permanent rejection, and 552 can point to mailbox or size-related problems, depending on how the receiver phrases its reply.

    Practical rule: read the human message first, then the code, then the technical detail.

    How to spot the useful parts quickly

    Look for the original recipient address if it appears. That helps you separate a typo from a stale contact. Look for the reporting server name. That shows which mailbox provider made the decision. Then read the reason phrase. That usually tells you whether the failure came from content, trust, or availability.

    The same code can still appear with different wording across providers. Gmail may return a 550-5.7.1 code with a policy explanation, while Microsoft often phrases a similar rejection as 550 5.7.1 Access denied. The number tells you the class of failure. The wording tells you what the provider cared about.

    For header reading, this guide helps: how to read an email header and spot a fake sender.
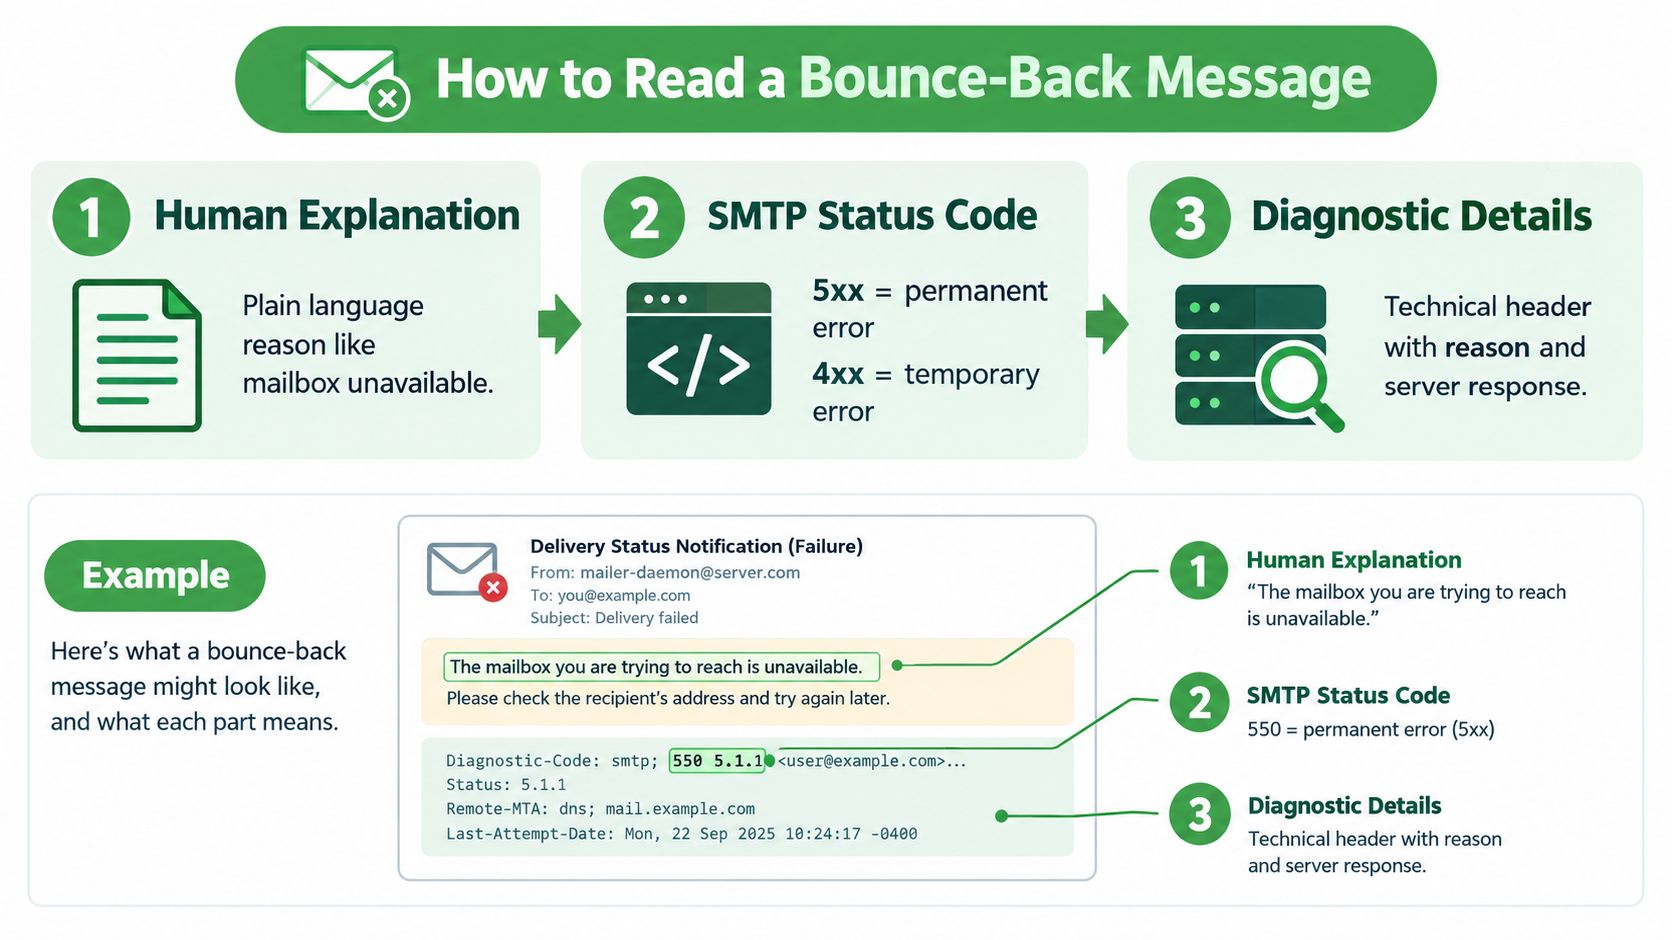
    An infographic explaining how to interpret email bounce-back messages using human explanations, status codes, and diagnostics.

    The Canadian Centre for Cyber Security notes that DMARC policy can be set to none, quarantine, or reject, and that a p=reject policy causes the message to be rejected or bounced back to the sender (ITSP.40.065 v1.1). A bounce can reflect policy enforcement, not just a bad address. That is why low bounce counts can still hide inbox placement trouble. Authentication and consent work on the root cause, not just the symptom.

    How to reduce your bounce rate

    A lower bounce rate starts before the send button is pressed. Clean lists, strong authentication, and steady sending habits all pull in the same direction. If one weakens, the others have to do extra work.

    Build cleaner lists from the start

    Double opt-in helps because it confirms that the person who signed up wants your mail. That lowers bad addresses and cuts down on low-quality contacts. Regular verification and suppression handling do the rest, especially when old addresses keep surfacing as failures.

    Consent matters here too. A list built with care is less likely to contain abandoned inboxes, fake signups, or people who never wanted your messages. Better consent usually leads to better engagement, and better engagement supports inbox placement.

    Authenticate before you scale

    The Canadian Centre for Cyber Security's guidance, cited above, advises SPF and DKIM on all domains, DMARC monitoring, and annual DKIM key rotation. That setup takes time, but it gives receiving servers a clearer trust signal.

    On a provider with unlimited sending, volume growth is not capped, so list quality and authentication become the primary constraints. You do not run into a provider-side sending wall that interrupts launches or campaigns. The limit shifts to how well you manage your audience and your domain signals.

    Warm up send volume with care

    Sudden bursts from a cold sending pattern can look suspicious. A gradual warm-up helps mailbox providers see steady behaviour instead of a spike that resembles abuse. That matters for small businesses that send in batches rather than on a fixed schedule.

    Typewire is one option in this space because it runs its own infrastructure in Vancouver and hosts email in Canada under Canadian privacy law. That can help teams keep mail under domestic jurisdiction while they work on authentication, consent, and list hygiene.

    Monitoring deliverability and next steps

    Bounce rate is only one metric to watch. You also need inbox placement, spam placement, and missing mail, because a message can fail without ever bouncing. That's the main reason teams get misled by a low bounce number.

    A 2025 benchmark reported 86.7% inbox placement, 5.4% spam placement, and 7.9% missing mail for Canada, with Gmail at 94.4%, Microsoft at 78.9%, and Yahoo/AOL at 88.6% (Validity 2025 Benchmark Report). Those figures show why you should track results by mailbox provider instead of relying on a single overall number.

    What to watch month to month

    Start with a baseline for your own sending, then compare each campaign against it. Watch where delivery drops by provider, because one mailbox system may tighten filtering before the others do. DMARC reports and reputation tools help you see problems early, before they turn into repeated bounces or silent inbox loss.

    A healthy bounce rate can still hide a weak delivery path.

    If you want to connect authentication work to real delivery outcomes, this guide on sender authentication is a useful companion: email sender authentication and deliverability. It pairs well with the bounce-reading habits above because it helps you connect technical setup to inbox placement.

    FAQ: Email Bounces

    What's a normal bounce rate?

    Canadian email benchmarks put the average hard bounce rate around 0.27% to 2.19%, depending on list age and sending frequency. That sounds low, but it masks the bigger picture. The same benchmarks show that 15 to 20% of emails still miss the inbox because of trust, relevance, and filtering issues, even when they don't bounce. A low bounce count doesn't mean strong deliverability. It just means the message reached the receiving server. Focus on inbox placement rates by provider, not bounce rate alone.

    What's the difference between a bounce and a message going to spam?

    A bounce means the receiving server rejected the message during delivery and sent it back. A spam filter means the server accepted the message but filed it away from the inbox. A bounce is fast, visible feedback. A message in spam is silent. You might never know it happened unless the recipient complains. That's why bounce rates can look healthy while inbox placement crumbles. Both are deliverability problems, but they need different fixes.

    How many times should I retry a soft bounce before giving up?

    Retry soft bounces once or twice over the next 24 to 48 hours. If the same contact bounces three times in a row for the same reason, treat it like a hard bounce and suppress it. A mailbox that stays full for a week usually has a bigger problem. Don't waste sending volume on an address that keeps failing. List quality matters more than retry volume.

    Why do I need to worry about bounces if my provider handles them?

    Your provider can log bounces and flag them, but you own the decision about whether to retry or remove an address. More importantly, repeated bounces hurt your sender reputation over time. If your list contains hundreds of invalid addresses that keep bouncing, mailbox providers start viewing your domain as less trustworthy. Clean lists protect your domain reputation. Providers give you the tools, but you drive the hygiene.

    Can better authentication actually reduce my bounce rate?

    Not directly. Authentication (SPF, DKIM, DMARC) doesn't stop bounces caused by bad addresses or full mailboxes. What it does is prevent bounces caused by trust failures. Some messages bounce because the receiving server doesn't trust the sender, not because the address is bad. Strong authentication tells servers "this mail is legitimate," so they're less likely to reject it upfront. The Canadian Centre for Cyber Security recommends SPF and DKIM on all sending domains for this reason.

    Should I use double opt-in to reduce bounces?

    Yes. Double opt-in confirms that the person who signed up actually wanted your mail and that the address is real. Single opt-in lists often contain typos, fake addresses, and low-quality signups. Double opt-in costs you a few initial subscribers, but the list you build is cleaner and delivers better. That means fewer bounces, better engagement, and stronger inbox placement overall.

    If I host email in Canada, does that change how I handle bounces?

    No, the bounce mechanics stay the same. SMTP standards are universal. What changes is that Canadian hosting under PIPEDA gives you clearer jurisdiction and control over your data while you manage list quality and authentication. Canadian providers like Typewire also mean you're not subject to U.S. government access to your sending records. The technical handling of bounces stays the same, but the privacy and compliance context improves.

    How do I know if a bounce is caused by my domain authentication or my list quality?

    Read the bounce message wording first. If it says "user does not exist" or "no such mailbox," it's a list quality problem. Remove the address. If it says "access denied," "policy violation," or "authentication failed," it's likely a domain trust problem. Check your SPF, DKIM, and DMARC setup. You can also use DMARC reports and email authentication monitoring tools to see which messages are failing due to policy enforcement versus bad addresses.

    For Canadian teams, the larger lesson is practical. Good bounce handling, better authentication, and stronger consent practices keep mail cleaner under PIPEDA-aware operations and make it easier to spot real problems early. If you want private email infrastructure that keeps your mail in Canada and gives you room to manage deliverability properly, visit Typewire and see how our email service fits small business sending, custom domains, and privacy-first operations.
  • Which Secure Email Provider Fits Your Workflow? 10 Options by Use Case

    Which Secure Email Provider Fits Your Workflow? 10 Options by Use Case

    Last updated: 24 September 2026

    Not all secure email providers are built for the same problems. A healthcare clinic needs different things than a privacy activist. A distributed team needs different tools than a single founder. A family needs different considerations than an open-source collective.

    The mistake most buyers make is treating email as a single category. You pick "the best" provider by some abstract standard, then spend the next six months frustrated because the product doesn't match how you actually work.

    This guide does the opposite. We've grouped 10 secure email providers by the specific workflows and concerns they solve. Find your use case, then read about the provider that's built for it.

    Find Your Use Case

    Which of these describes your situation?

    • Canadian SMB wanting local data and unlimited sending – Typewire

    • Healthcare or legal practice needing compliance docs – Hushmail

    • Team comfortable with standard email clients – PolarisMail

    • Individual prioritizing privacy over convenience – Tuta

    • Power user managing multiple identities – StartMail

    • Small team wanting encryption without locking in – Mailfence

    • EU-based team wanting comprehensive tools – mailbox

    • Family or transparency-focused organization – Runbox

    • Open-source-committed team – Kolab Now

    • User wanting mature encrypted ecosystem – Proton Mail

    Use Case Provider Primary Strength Hosting Price Level
    Canadian SMBs Typewire Local infrastructure + unlimited sending Vancouver $ (starts $0.80)
    Healthcare/Legal Hushmail Compliance docs + HIPAA BAA Vancouver $$ (starts $16.99)
    Standard clients PolarisMail IMAP/SMTP without friction Montreal $ (affordable)
    Privacy activists Tuta E2E by default, open-source Germany Free + paid
    Multiple identities StartMail Unlimited aliases Netherlands $$ (paid only)
    Mixed encryption Mailfence PGP + compatibility Belgium Free + paid
    EU teams mailbox All-in-one suite Germany $$ (paid)
    Families Runbox Sub-accounts, transparency Oslo $ (paid)
    FOSS advocates Kolab Now Full FOSS stack Switzerland $ (paid, first month free)
    Encrypted ecosystem Proton Mail Mature platform + suite Switzerland/EU Free + paid

    1. Canadian SMBs Wanting Local Infrastructure: Typewire

    You need your data hosted in Canada, operated by Canadians, with unlimited sending and practical business features. You don't want to fight your email provider to get basic work done.

    Typewire is the only email provider that owns and operates its own servers in Canada. Unlike competitors that rent infrastructure from Amazon, Google, or Microsoft, Typewire controls everything from hardware to security to data storage.

    In practice, that means:

    Your data isn't stored on AWS, Google Cloud, or Azure. It lives on Typewire's servers in Vancouver.

    No U.S. company involved. No CLOUD Act exposure. No reliance on foreign tech giants.
    Typewire makes every decision about your data security, not a cloud provider answerable to American shareholders.

    In January 2026, Canadian technology reviewer Frank Ring at Fraxoweb evaluated Typewire and wrote: "Typewire is the closest alternative that we have to Proton Mail in Canada. I wanted to support the Canadian economy and have all my data remain in Canada under Canadian laws."

    Why Typewire works for this use case

    A lot of people leave big platforms for privacy, then get stuck with a service that feels too restrictive to use every day. Typewire was built to avoid that trade-off. You can keep a privacy-first setup without giving up practical admin features like aliases, search, filters, mobile access, migration help, and team management.

    Gmail is a useful contrast here. Google Workspace documents a daily cap of 2,000 messages per user account, with 1,500 for mail merge and 500 for trial accounts. If you've ever hit a sending wall during a busy week, you already know why "unlimited sending" isn't just marketing copy.

    How the encryption works

    Typewire protects your data using zero-access storage encryption. Your data is encrypted in storage on Typewire's servers so that even Typewire's administrators cannot access it. Your encryption keys are protected with your private password that only you know.

    Most email providers use TLS encryption (data encrypted in transit) plus encryption at rest. But the provider holds the encryption keys, meaning they can technically access your email if compelled by court order. Because Typewire protects your encryption keys using your private password, even Typewire staff cannot access your email, regardless of legal requests. ProtonMail uses the same zero-access approach.

    Key features

    • Zero-access encryption (not even Typewire staff can read your emails)

    • Option to add end-to-end encryption for all messages

    • Spy pixel blocking by default

    • Advanced anti-spam and anti-phishing filters

    • Custom domain support on select paid plans

    • Team management for small businesses

    • PIPEDA-compliant by design

    • 7-day free trial (credit card required to start, cancel anytime within 7 days)

    • Webmail application supports both English and French

    • Two-factor authentication

    Pricing

    Starting at CA$0.80 per month, with commonly referenced paid plans around CA$5.11 per month for custom domains and unlimited sending.

    Pros: Only Canadian provider with owned servers, PIPEDA-compliant by design, strong encryption and privacy by default, unlimited sending on paid plans, bilingual interface.

    Cons: Smaller ecosystem compared to international providers, no free tier, limited feature breadth compared to all-in-one suites.

    Website: https://typewire.com

    2. Healthcare or Legal Practice Needing Compliance Documentation: Hushmail

    You're handling sensitive client information. You need verifiable compliance credentials, not just privacy marketing. Your provider needs to speak the language of secure portals, forms, and privacy documentation.

    Hushmail specializes in secure email for professionals handling regulated information. It's built specifically for healthcare, legal, and financial sectors that require verifiable HIPAA and PIPEDA compliance.

    Hushmail's entire product is built around compliance: HIPAA-compliant plans, Business Associate Agreements (BAAs), secure web forms for client intake, and e-signatures. This makes it the go-to choice for organizations that need email encryption bundled with compliance documentation.

    Where Hushmail stands out

    No other provider here offers HIPAA BAA documentation as standard. If your work involves handling regulated information or serving U.S. healthcare clients, Hushmail has built its entire product around these requirements.

    It isn't the cheapest option, and it isn't fully open source. You should also go in with realistic expectations about jurisdiction. A local provider still operates within lawful court processes. That's not a flaw unique to Hushmail. It's just part of choosing a provider in any real legal system.

    Key features

    • OpenPGP encryption

    • HIPAA-compliant plans with BAA support

    • Secure web forms with e-signatures

    • Email archiving for compliance

    • Custom domain support

    • Two-factor authentication

    Pricing

    Paid-only (no free tier). Healthcare Basic starts at CA$16.99 per month.

    Pros: Industry-specific solutions for HIPAA and legal compliance, secure web forms for sensitive data collection, e-signature support, strong compliance credentials, Canadian-based.

    Cons: No free tier, specialized for regulated use cases, higher pricing than general providers.

    Website: https://hushmail.com

    3. Teams Wanting Standard Email Clients: PolarisMail

    You want your email hosted in Canada, but you don't want to force everyone into a new app or learning curve. Your team uses Outlook, Apple Mail, or Thunderbird. That's fine. PolarisMail fits.

    PolarisMail takes a conventional hosting approach. Mail is stored on servers in Montreal, and the service focuses on dependable IMAP and SMTP email hosting for businesses and individuals. If your priority is "keep mail in Canada, but don't force everyone into a new app culture," PolarisMail is straightforward.

    That matters because a lot of migrations fail on habit, not policy. Teams get used to a familiar client, and switching disrupts workflow. PolarisMail fits those expectations better than providers built around custom encrypted apps.

    Best for standard email workflows

    This is a practical choice for businesses wanting local residency and straightforward email administration more than deep mailbox cryptography. You get standard client compatibility, spam and virus filtering, calendars, contacts, and business-friendly plans. It also offers white-label and reseller options, which can matter for agencies or IT providers.

    The trade-off is clear. PolarisMail isn't a zero-knowledge or end-to-end-by-default service. If your threat model centres on reducing provider-side access to mailbox contents, it won't rank as high as Typewire, Proton Mail, or Tuta.

    Still, there's value in a service that doesn't overcomplicate email. Many organisations need conventional hosted mail under local jurisdiction, with less friction than a more locked-down privacy product.

    Pricing

    Competitive and affordable tiers for businesses and individuals.

    Pros: Canadian hosted (Montreal), standard IMAP/SMTP support, affordable business plans, straightforward administration.

    Cons: Not a zero-knowledge or end-to-end-by-default service, less privacy-focused than encrypted-first alternatives.

    Website: https://polarismail.com

    4. Privacy Activists Willing to Leave Familiar Apps: Tuta

    You're leaving Gmail or Outlook because you're uncomfortable with how your data is used. You're willing to accept a new app environment to get real encryption by default.

    Tuta takes one of the strictest approaches to private email available. It's based in Germany, encrypts mail, contacts, and calendar by default inside its own environment, and keeps a strong privacy-first posture with open-source clients.

    The big trade-off is also the reason some privacy-focused people love it. Tuta deliberately doesn't support IMAP or POP. That preserves its encryption model, but it also means you need to use Tuta's apps and workflows.

    Best when you accept the app lock-in

    For some users, that's a dealbreaker. For others, it's exactly the point. You aren't buying compatibility first. You're buying a service designed around end-to-end privacy before convenience.

    This makes Tuta a strong choice for people leaving Gmail or Outlook for privacy reasons, especially if they don't need old desktop habits. It can also work for small teams willing to standardise on the same environment.

    The downside shows up during migration. If you rely on existing mail clients, unusual archive workflows, or standardised IT support documents, Tuta asks you to change more of your process than most alternatives here.

    Pricing

    Free tier available, with paid options for custom domains and aliases.

    Pros: End-to-end encryption by default, open-source clients, strong privacy-first posture, minimal telemetry.

    Cons: No IMAP or POP support, requires using Tuta's app ecosystem, migration can be disruptive to existing workflows.

    Website: https://tuta.com

    5. Power Users Managing Multiple Identities: StartMail

    You maintain separate email identities for shopping, newsletters, side projects, and client work. You want privacy hygiene through account separation, and you don't want to manage a complex suite.

    StartMail sits in a useful middle ground. It focuses on email rather than a giant suite, offers OpenPGP support, allows password-protected messages to non-users, and gives you unlimited disposable aliases.

    For readers who want strong privacy hygiene and lots of account separation, that alias model is a real strength. Disposable aliases limit exposure when one address starts attracting spam or unwanted tracking. That's a practical security gain, even though it isn't the same thing as end-to-end encryption.

    The alias-heavy option

    StartMail works well if you maintain multiple identities for shopping, newsletter signups, side projects, or client intake. Disposable aliases limit exposure when one address starts attracting spam or unwanted tracking. That's a practical security gain, even though it isn't the same thing as end-to-end encryption.

    The service also feels more email-focused than many competitors that bundle storage, meetings, and office tools. That focus can be refreshing. It can also feel limited if you were hoping to replace several products at once.

    Pricing

    Paid only (no free tier), with custom domain support.

    Pros: OpenPGP support, unlimited disposable aliases, password-protected messages, email-centric (no suite bloat).

    Cons: No free tier, Netherlands-based (not Canadian), requires discipline to manage multiple aliases effectively.

    Website: https://startmail.com

    6. Small Teams Wanting Encryption Without Locking In: Mailfence

    You want your team to use encryption and OpenPGP, but you don't want to force everyone into a proprietary app ecosystem. You want flexibility to add encryption to standard workflows.

    Mailfence balances security with compatibility better than many privacy-first tools. It's based in Belgium, supports OpenPGP in the browser, includes key management and digital signatures, and still works with standard IMAP and SMTP for ordinary mail workflows.

    That mix matters for teams that need flexibility. Pure zero-access services can be elegant, but they also break familiar habits. Mailfence gives you more room to combine standard email use with selective encrypted communication.

    A practical compromise for mixed environments

    The trade-off is that mailbox content isn't zero-knowledge by default. End-to-end privacy depends on using PGP correctly, which means more user responsibility. In practice, that often leads to uneven adoption inside teams.

    For that reason, we'd place Mailfence above simpler commodity hosts for privacy, but below stricter encrypted platforms for users with higher sensitivity needs. It's often strongest where one person on the team cares about privacy, while the rest still need normal mail behaviour.

    Pricing

    Freemium model with paid plans available.

    Pros: OpenPGP in-browser, key management and digital signatures, IMAP/SMTP support, integrated suite with admin tools.

    Cons: Mailbox content isn't zero-knowledge by default, requires user discipline for PGP adoption, not Canadian-based.

    Website: https://mailfence.com

    7. EU-Based Teams Wanting Comprehensive Tools: mailbox.org

    You need more than email. You want a privacy-oriented service with office tools, drive, and meetings all in one. You're comfortable with European hosting and procurement.

    mailbox.org is a stronger fit than many people expect if you want a privacy-oriented service with business-like breadth. It's hosted in Germany, supports PGP and S/MIME through mailbox.org Guard, and adds a wider workplace layer with office, drive, and meet features.

    This is not the provider for someone who wants a stripped-down inbox. It's for teams that want a serious alternative to mainstream suites without giving up collaboration features.

    Good depth, less local relevance

    mailbox.org also publishes certifications such as ISO 27001 and BSI C5, which some teams will value in procurement conversations. For organisations that need more than mail, that can carry more weight than a broad privacy slogan.

    The downside is obvious from a local buying lens. It isn't hosted in Canada, and parts of the interface feel oriented toward European business buyers. That doesn't make it hard to use. It just means the fit is stronger if your priority is a feature-rich private suite, not domestic hosting.

    Pricing

    Paid tiers with competitive pricing for comprehensive feature set.

    Pros: Feature-rich suite (mail, office, drive, meet), PGP and S/MIME support, ISO 27001 and BSI C5 certified, ad-free.

    Cons: Not Canadian-hosted, oriented toward European buyers, overkill for email-only users.

    Website: https://mailbox.org

    8. Families and Transparency-Conscious Organisations: Runbox

    You want privacy without abandoning standard mail tools. You want transparent operator practices and straightforward server ownership. You might need sub-accounts for family members or teams.

    Runbox appeals to a specific kind of buyer. It owns and operates its servers in Oslo, supports standard IMAP and SMTP, offers custom domains and sub-accounts, and presents a fairly transparent independence story.

    If you want privacy without abandoning standard mail tools, Runbox is easy to shortlist. Its family and team structure is also useful. Sub-accounts can make more sense than separate standalone plans when a household or a small firm wants one administrative umbrella.

    Straightforward and infrastructure-conscious

    Runbox doesn't offer built-in zero-knowledge mailbox privacy in the same way Proton or Typewire do. If you want end-to-end protection, you'll usually add PGP through clients and user practices. That makes it more compatible, but less automatic.

    Some people will also find the interface a bit less polished than newer privacy services. We wouldn't call that fatal. We'd just say the product prioritises independence and function over sleek packaging.

    Pricing

    Paid plans with migration help included.

    Pros: Server ownership and operation transparency, IMAP/SMTP support, sub-accounts for families and teams, affordable plans.

    Cons: Not zero-knowledge by default, interface less polished than newer competitors, not Canadian-hosted.

    Website: https://runbox.com

    9. Open-Source-Committed Teams: Kolab Now

    You prefer transparent software stacks. You want collaborative tools under one roof and you value open-source alignment more than location.

    Kolab Now is best understood as an open-source groupware service with privacy values, not just a secure mailbox. It's hosted in Switzerland, built on a fully FOSS stack, and includes mail, calendar, contacts, tasks, and files for both individuals and teams.

    That open-source alignment matters for some organisations more than location does. If your team prefers transparent software stacks and wants collaborative tools under one roof, Kolab Now deserves attention.

    Better for groupware than pure inbox simplicity

    The service gives you custom-domain support, admin controls, and modular add-ons, which is useful for teams that don't want an oversized enterprise suite. It also offers a first-month free option, which lowers the friction of testing workflows before a full migration.

    The limitation is familiar by now. It isn't locally hosted, and end-to-end privacy usually depends on client-side PGP rather than a built-in zero-access mailbox model. For many teams, that's acceptable. For organisations focused narrowly on secure email providers in Canada, it usually won't be the final choice.

    Pricing

    Paid plans with first month free to test.

    Pros: Fully FOSS stack, full groupware (mail, calendar, files, tasks), modular add-ons, admin controls for teams.

    Cons: Not Canadian-hosted, end-to-end privacy requires client-side PGP, overkill for email-only needs.

    Website: https://kolab.now

    10. Users Wanting Mature Encrypted Ecosystem: Proton Mail

    You've made privacy your top priority. You want the most mature, polished encryption-first platform available, and you're comfortable with Swiss hosting instead of Canadian.

    Proton Mail is one of the strongest mainstream privacy options available, even if it isn't hosted in Canada. It runs on Proton infrastructure in Switzerland, Germany, and Norway, and it offers a mature zero-access design, polished apps, custom domains on paid plans, and a larger ecosystem that includes Calendar, Drive, Pass, and VPN.

    That broader ecosystem is either a strength or a drawback. Some users like having everything in one place. Others would rather keep email separate so one vendor doesn't become their entire digital stack.

    Strong privacy model, more moving parts

    Proton is a good fit if you want a mature encrypted platform and are comfortable adapting to Proton's way of doing things. The biggest compatibility issue is desktop access through Proton Bridge if you want IMAP or POP in a third-party client. For some users that's acceptable. For others, it adds one more layer to troubleshoot.

    The service is also outside Canadian jurisdiction, which may matter for procurement or internal policy even if the privacy design is strong. That's why Proton often wins on encryption reputation but loses on local-hosting requirements.

    A useful rule of thumb is this. If you want a local email host, Proton probably isn't your first pick. If you want a mature encrypted suite and can accept its client model, it remains one of the safest recommendations available.

    Pricing

    Free tier available, with paid plans for additional storage and features.

    Pros: Unmatched privacy credentials, Swiss jurisdiction with strong privacy laws, integrated ecosystem (mail, calendar, VPN, drive), transparent and open-source, polished apps.

    Cons: Swiss-based, not Canadian, requires Proton Bridge for third-party clients, more expensive than some Canadian alternatives.

    Website: https://proton.me

    Before You Choose

    Check these details that buyers often skip:

    • Hosting location: Where the data sits physically.

    • Legal jurisdiction: Which laws and disclosure rules apply.

    • Access model: Whether the provider uses zero-access storage or relies on client-side PGP for stronger privacy.

    • Compatibility: Whether you need IMAP, SMTP, mobile apps, or Outlook and Apple Mail support.

    • Domain authentication: Whether the provider helps you set up SPF, DKIM, and DMARC properly.

    • Recovery design: How password resets, backup codes, and account recovery are handled.

    • Support quality: Whether you can get migration help from a human when mail flow breaks.

    • Total plan cost: The price once you include domains, aliases, users, and any required extras.

    How to Migrate

    Switching providers is usually less dramatic than people expect, but it goes badly when done in one big cutover. We recommend a staged move.

    • Export first: Move mail and contacts before changing DNS so you have a clean rollback path.

    • Stage DNS updates: Replace MX and authentication records methodically, not all at once.

    • Test deliverability: Send to and from common external services, then check headers and spam placement.

    • Notify contacts: Tell clients and staff about the change, especially if aliases or signatures will differ.

    • Keep the old account active: Leave it running until you've confirmed that all expected mail flow has moved.

    Fraud pressure is one reason to be careful. A 2024 TransUnion survey reported that about 54% of Canadians said they had been targeted by fraud attempts through email, phone, or text, and phishing was the top scheme type. A rushed migration is exactly when users miss spoofed messages, password resets, or forwarding loops.

    Frequently Asked Questions

    What's the difference between Canadian hosting and Canadian jurisdiction?

    Canadian hosting means your data physically sits on servers in Canada. Canadian jurisdiction means your provider operates under Canadian law (like PIPEDA) rather than US or European law. Canadian-hosted providers like Typewire, Hushmail, and PolarisMail offer both. International providers like Proton (Switzerland) offer strong privacy but operate under different legal frameworks.

    Do I need zero-access encryption, or is standard encryption enough?

    It depends on your threat model. Zero-access encryption (used by Typewire, Proton, and Tuta) means even the provider can't read your mail. Standard encryption with IMAP/SMTP support (used by PolarisMail, Runbox, and Mailfence) is easier to live with but requires client-side encryption for full privacy. For most small businesses, zero-access encryption is preferable but not essential if you trust the provider's security practices.

    Can I migrate to a new email provider without losing mail or breaking deliverability?

    Yes, if you do it in stages. Export mail and contacts first. Change DNS records methodically (MX, SPF, DKIM, DMARC) one at a time rather than all at once. Test sending and receiving before notifying everyone. Keep the old mailbox active until you've confirmed all expected mail is flowing to the new provider. This reduces the risk of missed invoices or customer emails.

    How do I know if a provider's encryption claims are real?

    Look for specific technical details: Does it support modern authentication (SPF, DKIM, DMARC)? Does it use TLS for transport security? For end-to-end encryption, does it support standard protocols like OpenPGP or S/MIME? Does it publish privacy policies and security whitepapers? Avoid providers that just say "secure" without explaining how.

    What if I want to switch providers later? Will I be locked in?

    A good provider makes switching easier by supporting standard email protocols (IMAP/SMTP) and helping you export mail and contacts. Providers like Typewire, PolarisMail, and Proton all support migration. Avoid providers with proprietary systems or unclear export options. Always ask about migration support before signing up.


    If you want email that stays in Canada, runs on privately operated infrastructure, and doesn't hit paid-plan sending walls, we built Typewire for exactly that use case. You can explore Typewire if you want a focused, ad-free alternative with custom domains, migration help, and privacy controls that make sense in everyday business use.